

The Able2Shell vulnerabilities highlights how endpoint management products can sometimes have vulnerability that allows for privileged access. Access that can potentially be further abused. Action1’s Endpoint Takeover Prevention (ETP) offers a way to address it, and we’re inviting N-able and other vendors to benefit from the architecture we’ve developed.
On November 9, N-able took its hosted N-central environments offline after publicly disclosing 33 vulnerabilities collectively known as Able2Shell. The disclosed attack chains could potentially allow threat actors to execute code, escalate privileges, and gain administrative control of N-central servers.
N-able acted quickly, taking precautionary measures to protect its customers. On November 10, the company released a security hotfix and restored its hosted environments. N-able reported scanning activity but no evidence of successful exploitation in customer environments.
We respect N-able’s decision to pause services, investigate, and put customer security first.
N-central Customers Are Asking the Right Question
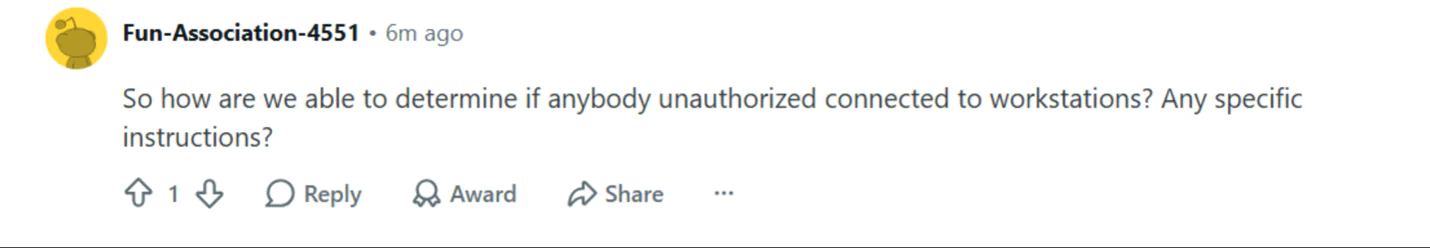
Following the disclosure, N-central customers raised an urgent question: “Are our endpoints safe? And how can we be certain?” The concern was evident in discussions on Reddit.
What if threat actors had successfully compromised N-central? Could they have used the platform to take over customer endpoints?
The Real Risk: From One Compromised Server to Millions of Endpoints
Endpoint management platforms require extraordinary privileges so they can execute scripts, deploy software, and open remote sessions across thousands of customer endpoints.
In traditional endpoint management architectures, endpoints implicitly trust commands from the management platform. That creates a dangerous possibility: a threat actor who gains control of the platform could potentially use its legitimate management capabilities to take over customer endpoints at scale.

The Able2Shell vulnerabilities illustrate how threat actors might gain that initial foothold on such a management system.
What If N-central Had ETP?
In October 2026, Action1 introduced Endpoint Takeover Prevention (ETP), an industry-first security architecture designed to prevent threat actors from using a compromised management platform to take control of customer endpoints.
ETP fundamentally changes the trust relationship between the platform and its endpoints.
Instead of automatically trusting high-risk commands delivered by the management platform, endpoints independently verify that the customer has authorized them.

Here’s how this could work in an environment, like N-central, if equivalent ETP protections were implemented:
- A threat actor compromises a centralized management plane. Through an exploited vulnerability, the threat actor gains administrative control of the management server.
- The threat actor attempts to take over customer endpoints. They try to deploy malicious software, execute scripts, or initiate unauthorized remote sessions.
- Endpoint agents reject unauthorized actions. Without valid cryptographic signatures created using customer-controlled private keys, the high-risk commands cannot execute through the protected management channel.
The threat actor may control the management platform, but platform control alone would not give them authority over customer endpoints.
That’s the fundamental difference ETP introduces. ETP Doesn’t Prevent Every Breach. It Prevents a Breach from Becoming an Endpoint Takeover.
ETP would not have fixed the Able2Shell vulnerabilities or prevented threat actors from exploiting the N-central server itself. Nor would it necessarily have eliminated the need for N-able’s precautionary shutdown.
What it could have done, if implemented throughout the relevant N-central management workflows, is prevent an threat actor who compromised the platform from using that access alone to execute unauthorized high-risk actions on managed endpoints.
That protection depends on customer signing keys remaining secure, endpoint agents enforcing signature verification, and the relevant operations being covered by the architecture.
The goal isn’t to assume that management platforms will never be compromised. It’s to ensure that compromising them doesn’t automatically compromise customer endpoints.
An Offer to N-able and the Entire Endpoint Management Industry
At Action1, we’ve spent three years developing ETP because we believe this architectural risk demands a fundamentally different approach to security.
Following the Able2Shell disclosure, Action1 CEO Alex Vovk reached out to N-able’s leadership with an offer to share the ETP architecture and connect our product teams to explore how similar protections could be implemented in N-central.
And our offer extends beyond N-able.
We’re inviting every endpoint management and RMM vendor to learn from our ETP architecture and work toward making endpoint takeover resilience an industry-wide standard.
We compete in the marketplace. But when it comes to protecting customers against cyberattacks, we believe the industry needs to work together.
Because no matter which endpoint management platform an organization chooses, a platform compromise should never automatically mean an endpoint takeover.
Request Access to the ETP Architecture: https://go.action1.com/call-for-collective-action-on-endpoint-takeover-resilience